

Cybersecurity
Google dismantles XCPE botnet: 1.3 million factory-infected Android devices neutralized
The tech giant revokes Videostrong’s license after finding malware pre-installed in its Android TV boxes and media players.
- Samsung Smart TVs standardly monitor audio and share data with 400 partners
- Is your Smart TV stealing your bandwidth behind your back?
- 1
Smuggling and drug trafficking shape the criminal landscape in Latin America’s Triple Frontier
- 2
Rolls-Royce turns to a £400m advanced manufacturing hub to strengthen Britain’s submarine industrial base
- 3
Vizio Smart TVs still track you even after you opt out
- 4
CISA warns of attacks exploiting WordPress vulnerability that allows hackers to take control of servers
- 5
US negotiates legal framework for troops in Caracas: What the plan covers and what it leaves out

- Alberto Payo
- Technology Journalist
- Published on
09 November 2026 at 06:15
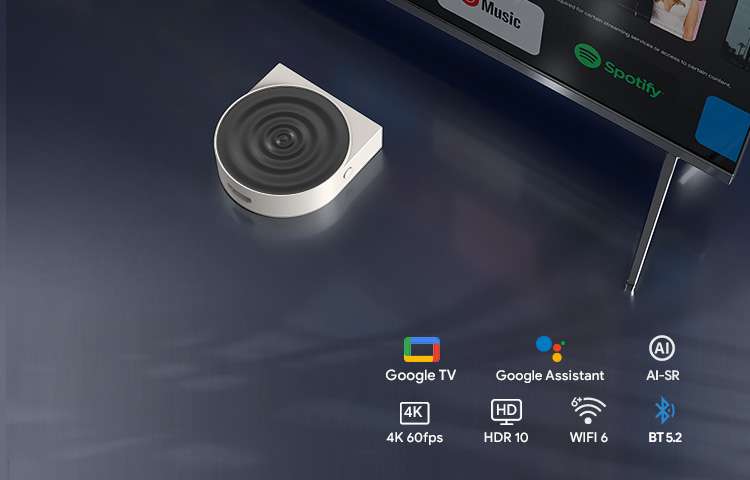
Google has managed to neutralize the infrastructure of XCPE, a botnet that controlled over 1.3 million Android-based devices globally.
The threat primarily affected media players and TV set-top boxes (Android TV set-top boxes), although cybersecurity analysts also detected the presence of this code in karaoke consoles, telemedicine terminals, and advertising screens.
The most striking aspect is that this time the malicious code was not introduced through everyday use or app downloads, but was integrated into the devices’ operating system (firmware).
Google’s Threat Intelligence team has linked this network to the hardware manufacturer Videostrong Technology. The Chinese company used this mechanism to monetize the devices after their sale, renting access to the infected network to third parties.
The software allowed the terminals to be transformed into nodes for unauthorized residential proxy networks, perform ad click fraud in the background, and execute espionage functions such as live screen capture, keystroke logging, and system metadata collection.
A threat that rose like the Phoenix
The malware stands out for its persistence within the equipment. Since it was part of the system package and located in the partition,it could survive a factory reset. Thus, even if the user tried to format the device, the backdoor would automatically reinstall during the boot process.
Additionally, to evade traditional detection systems, the system downloaded secondary components from repositories hosted on GitHub.
As a result of this threat, the Mountain View companyhas decided to revoke official Android certifications from Videostrong and its associated brands. The tech giant didn’t hesitate to also block their ability to market new devices with its operating system license.
“Our priority is to protect the integrity of the Android ecosystem and ensure that users can trust the security of their devices from the moment they connect them,”highlighted the Google division.
Become a premium member for free!
You may be interested in
- CybersecuritySamsung Smart TVs standardly monitor audio and share data with 400 partnersAlberto Payo
- CybersecurityIs your Smart TV stealing your bandwidth behind your back?Alberto Payo
- CybersecurityUS targets Prince Group’s financial network to stop it laundering proceeds from cyber scamsJuan Carlos De la Torre
- CybersecurityCritical ChatGPT vulnerability allowed account hijacking via a single linkAlberto Payo
“;
$(“#container-comentar-comentarios”).html(respuesta);
} else if (data == 2) { //TIEMPO
var respuesta =
“No ha pasado aún un minuto desde tu último comentario. Espera un poco y podrás comentar de nuevo una noticia.
“;
$(“#container-comentar-comentarios”).html(respuesta);
} else if (data == 3) { //PALABROTA
var respuesta = “Por favor, utiliza un lenguaje correcto para comentar las noticias.”;
Swal.fire({
text: respuesta,
icon: “warning”
});
} else { //NO LOGUEADO
var respuesta =
“Lo sentimos, al parecer no tienes una sesión iniciada. Vuelve a Iniciar Sesión y podrás publicar este comentario.”;
Swal.fire({
text: respuesta,
icon: “warning”
});
}
},
error: function (request, error) {
//console.log(error);
}
});
}
function sumarPositivo(id_comentario, id_usuario) {
$.ajax({
type: “POST”,
xhrFields: {
withCredentials: true
},
url: `/api/sumar_reaccion_comentario.php?t=` +
generarCadenaAlfanumerica(),
data: {
tipo: ‘positivo’,
id_comentario: id_comentario,
id_usuario: id_usuario
},
success: function (data) {
//console.log(data);
if (data == 1) {
var likes = parseInt($(“#like_” + id_comentario + ” span”).text());
$(“#like_” + id_comentario + ” span”).text(parseInt(likes + 1));
}
},
error: function (request, error) {
//console.log(error);
}
});
}
function sumarNegativo(id_comentario, id_usuario) {
$.ajax({
type: “POST”,
xhrFields: {
withCredentials: true
},
url: `/api/sumar_reaccion_comentario.php?t=` +
generarCadenaAlfanumerica(),
data: {
tipo: ‘negativo’,
id_comentario: id_comentario,
id_usuario: id_usuario
},
success: function (data) {
//console.log(data);
if (data == 1) {
var dislikes = parseInt($(“#dislike_” + id_comentario + ” span”).text());
$(“#dislike_” + id_comentario + ” span”).text(parseInt(dislikes + 1));
}
},
error: function (request, error) {
//console.log(error);
}
});
}
function recargar_widgets_sesion() {
recargar_cabecero_sesion();
recargar_menu_sesion();
recargar_comentar_sesion();
recargar_comentar_comentar();
comprobar_user_sesion_215_articulo(0);
}
function iniciarSesion() {
var continuar = true;
var msg = “”;
var usuario_log = $(“#usuario_log”).val();
var password_log = $(“#password_log”).val();
var valor_periodico = $(‘#valor_periodico’).val();
// console.log(valor_periodico);
if (usuario_log.length == 0) {
continuar = false;
msg += “Es necesario rellenar el correo electrónico n”;
}
if (password_log.length == 0) {
continuar = false;
msg += “Es necesario rellenar la contraseña.n”;
}
if (continuar) {
$.ajax({
type: “POST”,
data: $(“#formulario_login”).serialize(),
xhrFields: {
withCredentials: true
},
url: `/api/login-user.php?t=` +
generarCadenaAlfanumerica(),
error: function () {
Swal.fire({
text: “No hemos podido conectar con el servidor. Vuelve a intentarlo en unos minutos.”,
icon: “error”
});
},
success: function (data) {
// console.log(data);
if ($.trim(data) == “1”) {
recargar_widgets_sesion();
$(“#modal-login .modal-action.modal-close.close-btn”).trigger(“click”);
$(“#usuario_log”).val(“”);
$(“#password_log”).val(“”);
if (window.location.href.includes(“area-usuario”)) {
// window.location.reload();
}
} else {
var respuesta =
“No hemos encontrado ningún usuario con el correo electrónico y la contraseña introducidos. Por favor, vuelve a intentarlo o recupera la contraseña pulsando el botón inferior.”;
Swal.fire({
text: respuesta,
icon: “warning”
});
}
}
});
} else {
Swal.fire({
text: msg,
icon: “warning”
});
}
}
function comprobar_user_sesion_215_articulo(es_premium) {
$.ajax({
type: “POST”,
xhrFields: {
withCredentials: true
},
url: `/api/comprobar_sesion_user.php?t=` +
generarCadenaAlfanumerica(),
success: function (data) {
console.log(“COMPROBADO SESION USUARIO ” + data);
if (data == 1) {
$(“#art-cuerpo-visible”).removeClass(“d-none”);
$(“#art-cuerpo-visible”).removeClass(“art-cuerpo-no-visible”);
$(“#art-cuerpo-visible”).addClass(“art-cuerpo-visible”);
$(“#art-cuerpo-visible-premium”).removeClass(“art-cuerpo-visible”);
$(“#art-cuerpo-visible-premium”).addClass(“d-none”);
$(“#banner-premium”).addClass(“d-none”);
} else {
// $(“#art-cuerpo-visible”).removeClass(“art-cuerpo-visible”);
// $(“#art-cuerpo-visible”).addClass(“art-cuerpo-no-visible”);
if (es_premium) {
$(“#art-cuerpo-visible”).removeClass(“d-none”);
$(“#art-cuerpo-visible”).removeClass(“art-cuerpo-no-visible”);
$(“#art-cuerpo-visible”).addClass(“d-none”);
$(“#art-cuerpo-visible-premium”).addClass(“art-cuerpo-visible”);
$(“#art-cuerpo-visible-premium”).removeClass(“d-none”);
$(“#banner-premium”).removeClass(“d-none”);
} else {
$(“#art-cuerpo-visible-premium”).removeClass(“art-cuerpo-visible”);
$(“#art-cuerpo-visible-premium”).addClass(“d-none”);
$(“#banner-premium”).addClass(“d-none”);
$(“#art-cuerpo-visible”).removeClass(“d-none”);
$(“#art-cuerpo-visible”).removeClass(“art-cuerpo-no-visible”);
$(“#art-cuerpo-visible”).addClass(“art-cuerpo-visible”);
}
}
}
});
}
function comprobar_user_sesion_215() {
$.ajax({
type: “POST”,
xhrFields: {
withCredentials: true
},
url: `/api/comprobar_sesion_user.php?t=` +
generarCadenaAlfanumerica(),
success: function (data) {
console.log(“COMPROBADO SESION USUARIO ” + data);
if (data == 1) {
$(‘.col-comparador-registro-login’).addClass(‘w-auto’)
} else {
$(‘.col-comparador-registro-login’).removeClass(‘w-auto’)
}
}
});
}
function cerrarSesion() {
$.ajax({
type: “POST”,
xhrFields: {
withCredentials: true
},
url: `/api/delete-session-user.php?t=` +
generarCadenaAlfanumerica(),
success: function (data) {
//console.log(data);
recargar_widgets_sesion();
$(“#offCanvasClose”).trigger(“click”);
if (window.location.href.includes(“area-usuario”)) {
window.location.href = ‘/’;
}
}
});
}
function registrarCuenta() {
var continuar = true;
var msg = “”;
var email_registro = $(“#email_reg”).val();
var pass_registro = $(“#password_reg”).val();
var pass_registro2 = $(“#password_reg_2”).val();
var nombre_registro = $(“#nombre_reg”).val();
var apellidos_registro = $(“#apellidos_reg”).val();
var ref_id_periodico = $(“#ref_id_periodico”).val();
if (pass_registro2 != pass_registro) {
continuar = false;
msg += “Deben coincidir ambas contraseñas. n”;
}
if (email_registro.length == 0) {
continuar = false;
msg += “Es necesario rellenar el correo electrónico. n”;
}
// if (pass_registro.length < 8) {
// continuar = false;
// msg += “Cal omplir la contrasenya amb un mínim de 8 caràcters. n”;
// }
if (nombre_registro.length == 0) {
continuar = false;
msg += “Hay que llenar el nombre. n”;
}
if (!$(“#aceptopoliticas”).is(“:checked”)) {
continuar = false;
if (ref_id_periodico == 8) {
msg += “You must accept the privacy policy. n”;
} else {
msg += “Debes aceptar la política de privacidad. n”;
}
}
if (continuar) {
$.ajax({
type: “POST”,
xhrFields: {
withCredentials: true
},
data: $(“#formulario_registro”).serialize(),
url: `/api/register-user.php?t=` +
generarCadenaAlfanumerica(),
success: function (data) {
if ($.trim(data) == “1”) {
var respuesta = “¡Enhorabuena! Te has registrado con éxito. Ya puedes iniciar sesión.”;
Swal.fire({
text: respuesta,
icon: “success”
});
recargar_widgets_sesion();
$(“#email_reg”).val(“”);
$(“#password_reg”).val(“”);
$(“#password_reg_2”).val(“”);
$(“#nombre_reg”).val(“”);
$(“#apellidos_reg”).val(“”);
} else {
var respuesta = “No hemos podido completar el registro. Revisa los datos introducidos; puede que este correo electrónico ya esté registrado.”;
Swal.fire({
text: respuesta,
icon: “warning”
});
}
},
error: function () {
Swal.fire({
text: “No hemos podido conectar con el servidor. Vuelve a intentarlo en unos minutos.”,
icon: “error”
});
}
});
} else {
Swal.fire({
text: msg,
icon: “warning”
});
}
}
function recuperarPass() {
$.ajax({
type: “POST”,
xhrFields: {
withCredentials: true
},
data: $(‘#formulario_recuperarpass’).serialize(),
url: `/api/reset-pass-user.php?t=` +
generarCadenaAlfanumerica(),
success: function (data) {
if ($.trim(data) == “1”) {
Swal.fire({
text: “Revisa tu e-mail y sigue las instrucciones para recuperar tu contraseña.”,
icon: “info”
});
$(“#modal-pass .modal-action.modal-close”).trigger(“click”);
$(“#email_recuperar”).val(“”);
} else {
Swal.fire({
text: “No hemos podido enviar el correo de recuperación. Comprueba que la dirección es correcta o inténtalo de nuevo más tarde.”,
icon: “warning”
});
}
},
error: function () {
Swal.fire({
text: “No hemos podido conectar con el servidor. Vuelve a intentarlo en unos minutos.”,
icon: “error”
});
}
});
}
function resetearPass() {
if ($(“#nuevo-pass”).val() == $(“#nuevo-pass-repeat”).val()) {
if ($(“#nuevo-pass”).val().length >= 8) {
$.ajax({
type: “POST”,
xhrFields: {
withCredentials: true
},
data: $(‘#resetear-clave’).serialize(),
url: `/api/resetear-pass.php?t=` +
generarCadenaAlfanumerica(),
success: function (data) {
//console.log(data);
$(“#email_recuperar”).val(“”);
var respuesta = “La contraseña se ha actualizado. Ya puedes volver a Iniciar Sesión.”;
Swal.fire({
text: respuesta,
icon: “success”
}).then((result) => {
window.location.href = ‘http://www.escudodigital.com/’;
});
}
});
} else {
var respuesta = “La contraseña debe tener un mínimo de 8 caracteres.”;
Swal.fire({
text: respuesta,
icon: “warning”
});
}
} else {
var respuesta = “Ambas contraseñas deben coincidir.”;
Swal.fire({
text: respuesta,
icon: “warning”
});
}
}
$(document).ready(function () {
recargar_widgets_sesion(); //DESCOMENTAR ESTO
});
‘)
.text(msg)
.insertAfter($el);
}
function esEmailValido(email) {
return /^[^s@]+@[^s@]+.[^s@]{2,}$/.test(String(email).trim());
}
function validar() {
limpiarErrores();
let ok = true;
const $nombre = $(“#nombre”);
const $email = $(“#email”);
const $motivo = $(“#motivo”);
const $check = $(“#checkbox”);
const nombre = $nombre.val().trim();
const email = $email.val().trim();
const motivo = $motivo.val().trim();
if (nombre.length < 2) {
marcarError($nombre, “Enter your full name.”);
ok = false;
}
if (!esEmailValido(email)) {
marcarError($email, “Enter a valid email.”);
ok = false;
}
if (motivo.length < 5) {
marcarError($motivo, “Briefly explain how we can help you.”);
ok = false;
}
if (!$check.is(“:checked”)) {
marcarError($check, “You must accept the legal terms.”);
ok = false;
}
return ok;
}
function setLoading(isLoading) {
$btn.prop(“disabled”, isLoading);
$btn.text(isLoading ? “Sending…” : “Sent”);
}
function submitFormWithToken(token) {
setLoading(true);
const payload = {
nombre: $(“#nombre”).val().trim(),
email: $(“#email”).val().trim(),
motivo: $(“#motivo”).val().trim(),
legal: $(“#checkbox”).is(“:checked”) ? 1 : 0,
periodico_id_periodico: 8,
periodico: ‘www.escudodigital.com’,
url: window.location.href,
periodico_nombre: ‘DigitalShield’,
token: token
};
$.ajax({
url: URL_ENDPOINT,
method: “POST”,
data: payload,
dataType: “json” // Expects JSON response from server
})
.done(function (res) {
if (res && (res === 1 || res === “1” || res.ok)) {
$(“#msgFormContacto”).html(‘Message sent successfully.
‘);
$form[0].reset();
} else {
$(“#msgFormContacto”).html(‘Message not sent. Try again.
‘);
}
})
.fail(function (xhr) {
$(“#msgFormContacto”).html(‘Connection error. Try again.
‘);
})
.always(function () {
setLoading(false);
});
}
$btn.on(“click”, function (e) {
e.preventDefault();
e.stopPropagation(); // Stop default button behavior if any
if (!validar()) return;
// Execute reCAPTCHA
if (window.grecaptcha) {
grecaptcha.ready(function () {
grecaptcha.execute(RECAPTCHA_SITE_KEY, {
action: ‘submit’
}).then(function (token) {
submitFormWithToken(token);
});
});
} else {
// Fallback or error if grecaptcha not loaded
alert(“reCAPTCHA not loaded. Please refresh.”);
}
});
$(“#nombre,#email,#motivo,#checkbox”).on(“input change”, function () {
$(this).removeClass(“is-invalid”);
$(this).next(“.error-text”).remove();
});
});
// funcion para detectar si el primer mega top existe el primer mega lo oculte
if ($.trim($(‘.BN-MEGATOP’).html()) !== ”) {
console.log(“entra”);
// 1. Busca el container-mega inmediatamente superior a TRIPLE_SUPERIOR
$(‘.TRIPLE_SUPERIOR’).first().prevAll(‘.container-mega’).first().addClass(‘d-none’);
// 2. CORREGIDO: Busca el primer container-mega DENTRO de .wrap-LISTADO
$(‘.wrap-LISTADO’).find(‘.container-mega’).first().addClass(‘d-none’);
}
