Close Menu
MyAppsPlus

    Subscribe to Updates

    Get the latest creative news from FooBar about art, design and business.

    What's Hot

    Yangwang U9 Xtreme breaks the 312mph barrier with battery packs and electric motors

    November 10, 2026

    WhatsApp now works better for people who don’t have the app

    November 10, 2026

    Hotel giant Wyndham exposed customer data after app security lapse

    November 10, 2026
    Facebook X (Twitter) Instagram
    Facebook X (Twitter) Instagram
    MyAppsPlusMyAppsPlus
    Tuesday, November 10
    • Home
    • Breaking Tech
    • Apps & Software
    • AI & Automation
    • Android
    • iPhone & iOS
    • More
      • Reviews
      • How-To Guides
      • Deals & Discounts
      • Shop
    MyAppsPlus
    Home»Reviews»Watch out — TP-Link Tapo Camera vulnerabilities could let hackers spy inside homes, so patch now
    Reviews

    Watch out — TP-Link Tapo Camera vulnerabilities could let hackers spy inside homes, so patch now

    myappsplusBy myappsplusSeptember 16, 2026024 Mins Read
    Share Facebook Twitter Pinterest Copy Link LinkedIn Tumblr Email Telegram WhatsApp
    Follow Us
    Google News Flipboard
    Watch out — TP-Link Tapo Camera vulnerabilities could let hackers spy inside homes, so patch now
    Share
    Facebook Twitter LinkedIn Pinterest Email Copy Link
    • Opswat found two flaws in TP‑Link Tapo C200 cameras: auth bypass (CVE‑2026‑15315) and DoS (CVE‑2026‑15316)
    • Bugs let attackers hijack admin sessions or crash devices; millions of users potentially exposed
    • TP‑Link patched with firmware V5_1.4.6 on Aug 18, 2026; users urged to update immediately

    Security researchers found a pair of vulnerabilities in popular smart cameras, which could allow threat actors to peep into people’s homes and businesses.

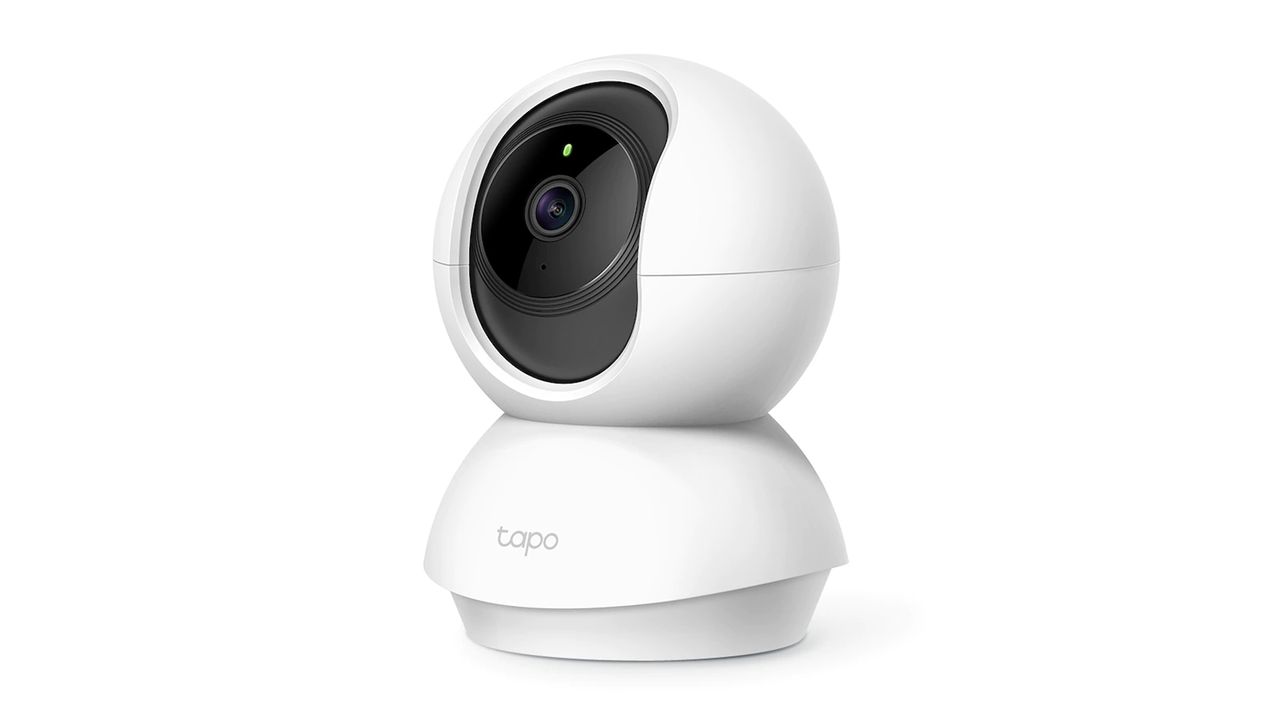
    Earlier this week, Opswat disclosed finding two bugs in the TP-Link Tapo C200 smart security camera – an authentication bypass flaw, and a denial-of-service vulnerability. The former is tracked as CVE-2026-15315 and was given a severity score of 8.7/10 (high). Opswat says the bug allows unauthenticated attackers to obtain valid admin sessions without having a password, which would allow them to manage the device and even watch the stream.

    The latter is tracked as CVE-2026-15316. With a severity score of 7.1/10 (high), this bug allows threat actors to send oversized crypted ciphertext values that may trigger exception handling failures and cause the affected device to crash or restart. “Successful exploitation may temporarily disrupt HTTPS management and monitoring functionality, resulting in a denial-of-service (DoS) condition until the service recovers,” according to the NVD.

    Patching the bugs

    The C200 is a mass-market product, advertised as a security camera, a baby monitor, or a pet camera, with motion detection, 1080p video, 2-way audio, night vision, cloud & SD card storage, and integrations with both Alexa and Google Home.

    Opswat disclosed their findings to TP-Link in mid-April this year, which started working on a fix in early July this year. On August 18, 2026, TP-Link released firmware version V5_1.4.6, which addressed both flaws. Users are advised to install the fix as soon as possible.

    The researchers did not discuss if the flaws were being abused in the wild, or to what extent. We do know that TP-Link Tapo cameras are rather popular, with the C200 model being relatively widely sold. According to TP-Link, the Tapo app has more than 13 million users, while the Google Play Store shows 10+ million downloads.

    On Amazon, the C200 specifically is listed as the #1 top rated product in its category, with more than 3,000 purchases this month alone.

    “Camera bugs always get attention because of the “spy factor,” but they usually sound cooler and scarier than they actually are,” said Dahvid Schloss, OSCP, Chief Operating Officer at Suzu Labs. “The main reason not to “worry” about this one is that running this exploit requires local network access, so a threat actor has to be on your Wi-Fi or already own a device that is.

    “If someone’s made it that far into your network, they’re not after the baby monitor. Now, if the camera was port-forwarded to the internet, that’s a bigger design issue and probably should be a concern, but not a common setup for the everyday home user. Either way, I’d still patch the camera, but it’s pretty low on the totem pole of what a cybercriminal wants.”

    “I’m quite curious about the undisclosed vulnerability that reportedly allows full compromise and a foothold to pivot from,” Schloss added. “Based on what was reported, I would guess the exploit would be a command injection or a memory-safety bug in the same management service, chained behind that auth bypass to get code execution as root, where they then dropped a static binary to return a shell on the device whose firmware ships with almost no tooling. That attack chain isn’t uncommon on cheap, older consumer IoT devices where security wasn’t top of mind, but if that’s the case here, seeing it hold up on a modern TP-Link device would be a bit of a blast from the past.

    Computing Computing Security Cyber Security Pro Security
    Follow on Google News Follow on Flipboard
    Share. Facebook Twitter Pinterest LinkedIn Tumblr Email Copy Link
    myappsplus
    • Website

    Related Posts

    WhatsApp now works better for people who don’t have the app

    November 10, 2026

    Hotel giant Wyndham exposed customer data after app security lapse

    November 10, 2026

    Dangerous new Gmail exploit lets hackers read your emails for a monthly fee of $1,000 — and it even works after a password reset

    November 10, 2026
    Add A Comment
    Leave A Reply Cancel Reply

    Top Posts

    Cathay Pacific tests Google AI that dramatically cuts airplane contrails — tiny altitude shifts slash environmental impact by 40% in early trials

    September 8, 2026138 Views

    Save on your groceries, gas, and holiday shopping with this $15 BJ’s membership (Reg. $60) 

    November 4, 202627 Views

    Apple is making Creator Studio an even better deal with new AI features and creative tools

    October 28, 202621 Views
    Latest Reviews

    OpenAI says it reached its goal of creating an automated research intern

    myappsplusSeptember 6, 2026

    Will the iPhone Ultra really be ‘Ultra’? 5 features the foldable could surprisingly ditch, from Face ID to MagSafe

    myappsplusSeptember 6, 2026

    Best TVs of 2026: Expert Tested, Compared and Reviewed

    myappsplusSeptember 6, 2026
    Stay In Touch
    • Facebook
    • YouTube
    • TikTok
    • WhatsApp
    • Twitter
    • Instagram

    Subscribe to Updates

    Get the latest tech news from FooBar about tech, design and biz.

    Most Popular

    Microsoft is ending Windows 11’s web app slop era, and AI now writes native apps in 30 minutes

    September 6, 20260 Views

    Is it safe to buy a refurbished iPhone from Walmart?

    September 7, 20260 Views

    I’m fixing my desk posture without doing a single back exercise — here’s the foot mobility trick a neurosurgeon taught me

    September 7, 20260 Views
    Our Picks

    Yangwang U9 Xtreme breaks the 312mph barrier with battery packs and electric motors

    November 10, 2026

    WhatsApp now works better for people who don’t have the app

    November 10, 2026

    Hotel giant Wyndham exposed customer data after app security lapse

    November 10, 2026

    Subscribe to Updates

    Subscribe to our newsletter and get the latest tech news, app updates, AI trends, smartphone reviews, and exclusive deals delivered straight to your inbox.

    Facebook X (Twitter) Instagram Pinterest
    • About Us
    • Get In Touch
    • Disclaimer
    • Privacy Policy
    • Terms & Conditions
    © 2026 MyAppsPlus. All Rights Reserved.

    Type above and press Enter to search. Press Esc to cancel.